An LED display access control plan should define who may view status, operate approved controls, change configuration, install updates, restore backups, and authorize emergency access. It should also show how every privileged action is approved, recorded, verified, and reversed if the result is wrong. The objective is simple: give each person enough access to do assigned work without turning a shared administrator account into the system’s default operating method.
Access control and change control belong together. Permissions decide who can act; change management decides when and how that action may occur. A technically valid adjustment can still create an outage if it is made against the wrong baseline, during a critical event, or without a recoverable backup. Buyers should therefore treat accounts, approvals, configuration records, and rollback evidence as part of the delivered LED system—not as informal habits added after handover.
What should an LED display access control plan include?
Direct answer: include a named system owner, an inventory of control surfaces, role definitions, unique accounts, authentication rules, permission boundaries, approval routes, emergency-access conditions, a change record, backup and rollback requirements, post-change testing, access-review intervals, and a clear process for staff or supplier changes. The plan should cover the complete operating path, not only the LED controller software.
- List every interface that can affect content, power state, brightness, schedules, processing, mapping, monitoring, firmware, or remote support.
- Assign an accountable owner and technical custodian for each system.
- Give named users the minimum permissions required for their role.
- Separate routine operation from configuration, maintenance, and administrative work.
- Define which changes require approval, a maintenance window, backup, witness, or supplier support.
- Record the request, reason, affected assets, baseline, implementer, test result, and rollback decision.
- Review accounts after role changes, contract changes, incidents, and scheduled intervals.
- Store recovery information securely and test that it can actually restore the accepted configuration.
Map the complete control surface first
The LED wall is only one part of the control boundary. A venue may also have a content-management platform, source computers, switchers, video processors, sending controllers, monitoring tools, smart power controls, remote-access software, network equipment, cloud portals, and vendor service accounts. If a person can change what the audience sees or how the system starts, routes, maps, or recovers, that interface belongs in the inventory.
Record the asset name, location, owner, platform, account type, supported authentication method, network dependency, backup location, and business impact. Use the same asset names found in the LED display as-built documentation. Consistent names make permissions, tickets, screenshots, and recovery instructions refer to the same equipment.
Assign permissions by role and task
LED wall role-based access means assigning capability to a defined job rather than giving every trained person administrator rights. A daily operator may select approved sources and presets. A shift lead may approve a documented degraded mode. Technical support may view diagnostics and collect logs. A qualified service role may change mapping or firmware within an approved work order. The business owner decides who receives those roles and who can approve exceptions.
On smaller screens, swipe horizontally to view all columns.
| Role | Normal access | Restricted action | Required evidence |
|---|---|---|---|
| Operator | Approved startup, shutdown, source and preset selection, status viewing | No mapping, firmware, calibration, account, or network changes | Named account and operator authorization |
| Shift lead | Operator functions plus approved escalation and operating-mode decisions | No technical change unless separately authorized | Shift decision or incident record |
| AV or IT support | Diagnostics, logs, baseline comparison, approved recovery steps | No unapproved production change | Ticket, captured baseline, and test result |
| Service technician | Assigned configuration, repair, update, and restoration tasks | No work outside the approved asset and window | Approved change record and service report |
| System owner | Role approval, risk acceptance, scheduling, and closure | Does not replace electrical, structural, or technical qualification | Approval and acceptance record |
The platform may not support perfect separation. When one account exposes both routine controls and advanced settings, document the limitation and add practical controls such as supervised access, locked workstations, approved presets, session logging, or a second-person check. Training supports the permission model but does not replace it; the operator training plan should teach the same boundaries.
Use unique accounts and controlled credentials
Unique accounts make it possible to remove access without disrupting everyone and to connect an action to an authorized person. Shared administrator credentials make that harder. Where the product supports it, use named accounts, strong authentication, session timeout, appropriate multi-factor authentication, and separate service or automation identities. Do not place reusable passwords in operator guides, labels, screenshots, or incident reports.
Some legacy processors or local utilities may support only one credential or no account separation. Record that fact as a system limitation. Restrict physical and network access, control the device that stores the utility, log each privileged session through the work process, and include improved account capability in the next upgrade decision.
Classify changes before approving them
LED display change management should distinguish routine, standard, normal, and emergency work in terms the organization can apply. A routine operator action follows an accepted procedure and does not alter the baseline. A pre-authorized standard change is repeatable and low risk but still recorded. A normal change needs review and approval. An emergency change addresses an urgent service or safety need, with shortened approval but not missing documentation.
Examples that normally deserve formal review include receiver-card mapping, calibration files, processor EDID or scaling, redundancy routing, controller replacement, firmware, network addressing, power schedules, remote-access configuration, and changes to monitoring thresholds. The exact category depends on business impact and system architecture, not only on how many clicks the task requires.
What belongs in a change request?
- A clear reason and expected outcome.
- Exact assets, interfaces, software, configuration items, and locations affected.
- Current accepted baseline and the proposed new state.
- Operational impact, dependencies, risks, and excluded work.
- Named requester, approver, implementer, witness, and acceptance owner where applicable.
- Maintenance window, communications plan, and event or business constraints.
- Backup method, rollback trigger, rollback steps, and time needed to recover.
- Pre-change checks, implementation sequence, post-change tests, and evidence to retain.
- Training, documentation, monitoring, or spare-parts updates created by the change.
A short form can be sufficient for a low-risk standard change. Higher-impact work needs more detail. The important point is that another qualified person can understand what will change, what must remain unchanged, how success will be measured, and when the team must stop or reverse the work.
Back up the accepted state before technical work
An LED display configuration backup is useful only when its source, scope, date, version, and restoration method are known. Export the relevant controller, processor, mapping, calibration, monitoring, or network configuration before the change where the equipment supports it. Preserve related files together with a readable manifest rather than relying on a folder full of unexplained exports.
Do not assume that an export contains every dependency. Some states may live in hardware, a different application, a cloud account, or a source device. Verify the restoration path in a controlled environment when practical, keep a protected accepted copy, and restrict access because configuration files may expose network details or operational information.
Use a controlled implementation sequence
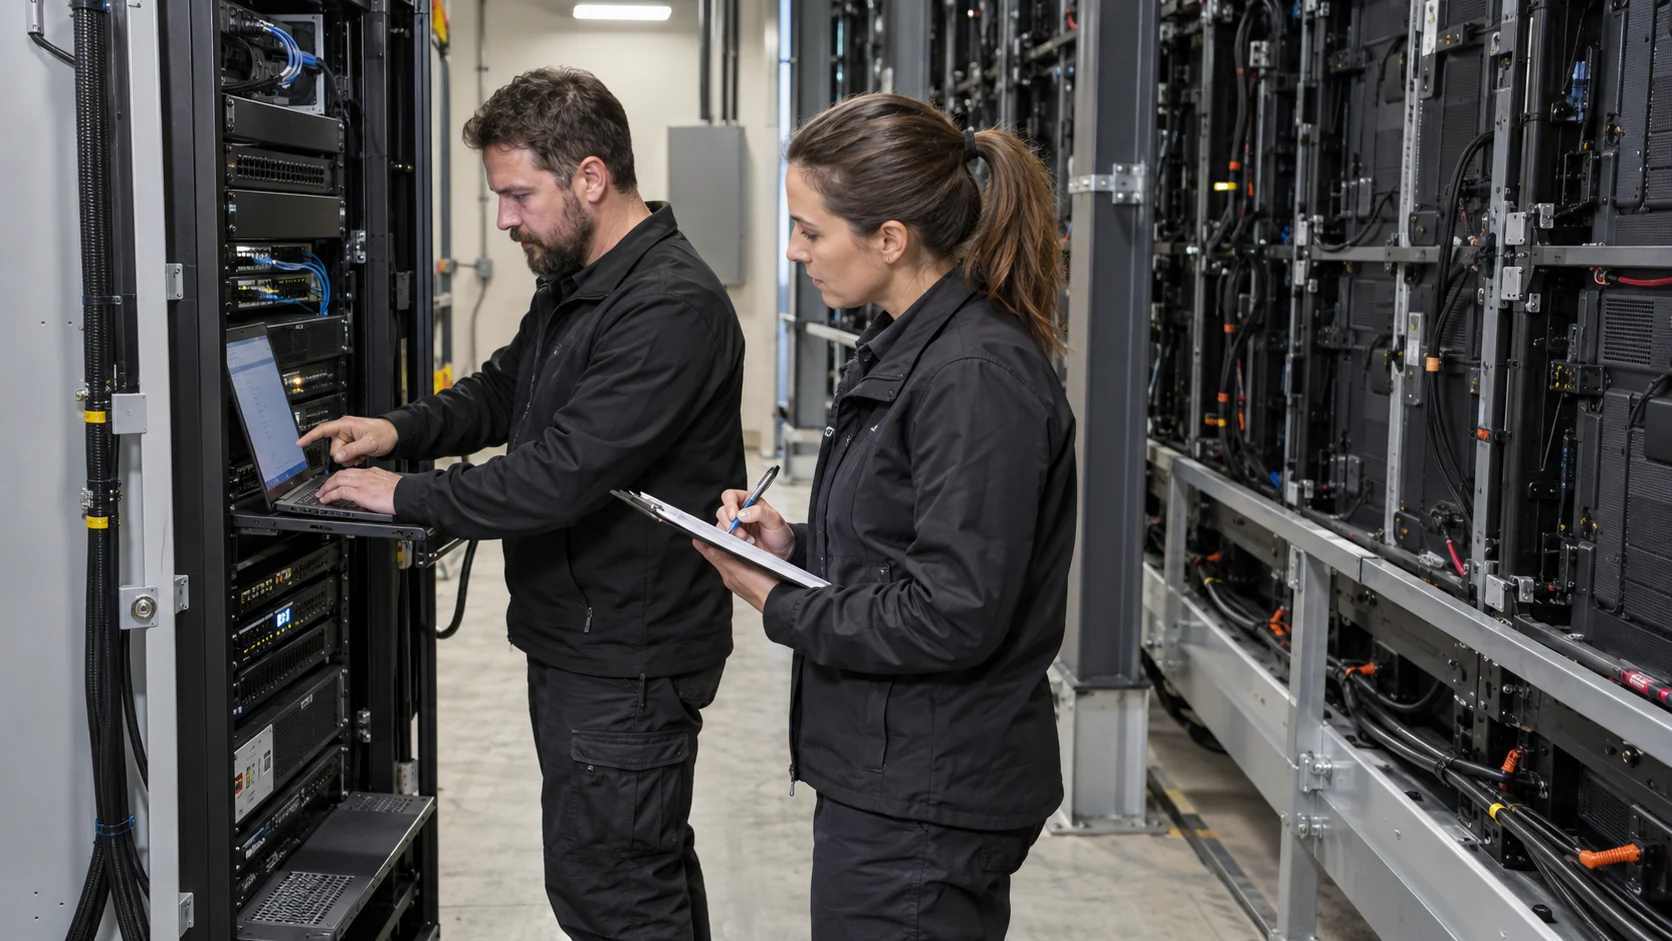
Before work starts, confirm the correct asset, approved window, current service state, communication route, backup, test content, and recovery resources. Pause if the live configuration differs from the recorded baseline. That mismatch may indicate an undocumented earlier change, and continuing can make the recovery point uncertain.
During implementation, change only the approved items and record material deviations. For high-impact work, a second qualified person can verify asset identity, file selection, critical values, and completion tests. Follow the project’s firmware update plan when software or device firmware is involved; compatibility and rollback preparation should be confirmed before production equipment is changed.
Test service, not just the settings page
A successful save message is not acceptance evidence. Post-change testing should confirm the visible canvas, intended resolution and scaling, approved sources and presets, color and brightness behavior, redundancy where included, monitoring status, startup and shutdown behavior, remote-support path, and any affected schedule or alarm. Test from the operator’s normal interface as well as the technical tool.
Record the result, screenshots or photos where appropriate, software and configuration versions, test content, exceptions, and the person who accepted service. If the change affects normal operation, update the startup and shutdown procedure before operators rely on the new state.
Define emergency access before an incident
Emergency access should be exceptional, time-limited, and attributable. Define who may authorize it, what qualifies as an emergency, how credentials are released, which actions remain prohibited, how the session is monitored or recorded, and when access is removed. If normal approval is unavailable, name the alternative authority in advance.
The immediate objective may be service restoration, but the team should still preserve the reason, actions, versions, evidence, and resulting state. Link the activity to the incident report, then review whether the emergency action becomes an accepted baseline, requires rollback, or needs a follow-up normal change.
Review access through the system lifecycle
An LED display access review should compare current accounts and privileges with current roles, training status, supplier contracts, support needs, and system ownership. Review immediately when a person changes role or leaves, a service provider changes, a shared credential may have been exposed, or an incident reveals excessive permission. Also set a periodic review interval appropriate to the organization and system criticality.
Remove dormant accounts, obsolete remote tools, duplicate administrators, and permissions that are no longer justified. Confirm that required recovery access still works and that ownership will not disappear when one employee or contractor is unavailable. Access removal should include local applications, cloud portals, VPN or remote-support routes, stored browser sessions, and physical keys where relevant.
What should buyers require at handover?
- Inventory of all control, monitoring, content, power, network, and remote-support interfaces.
- Account and role matrix showing permitted tasks and ownership.
- Documented credential-transfer process without passwords exposed in general manuals.
- Accepted configuration exports, file manifest, version references, and restoration procedure.
- Change-request, implementation, test, rollback, and closure templates.
- Emergency-access and vendor remote-support conditions.
- Account creation, modification, suspension, removal, and periodic-review responsibilities.
- Project-specific operator and technical training tied to permissions.
- Support escalation and maintenance scope aligned with the LED display maintenance SLA.
Questions about LED display access and changes
Should every operator have a separate account?
Named accounts are preferable when the platform supports them because access can be changed per person and actions are easier to attribute. If the product only supports a shared account, document the limitation and add physical, procedural, session, and supervisory controls.
Does changing brightness require formal approval?
An approved operator adjustment within a documented range may be routine. Changes to calibration, automatic schedules, power assumptions, safety constraints, or the accepted visual baseline may require formal review. Define the boundary in the operating procedure rather than deciding during an event.
Can a supplier keep permanent remote administrator access?
Remote support should follow the customer’s approved security and service model. Prefer named, limited, monitored, and revocable access with an agreed activation method and purpose. Buyers should know who can connect, when, through which route, what is logged, and how access ends with the contract.
When should an LED configuration be rolled back?
Define rollback triggers before implementation. Examples include failed acceptance checks, unexpected image behavior, loss of monitoring or redundancy, instability, an exceeded maintenance window, or discovery that the baseline was wrong. The authorized change owner should make the decision using the agreed criteria.
Who owns the final access plan?
The customer’s designated system or service owner should own operating authority and risk decisions. Integrators, manufacturers, IT teams, and service providers can supply technical requirements and implement controls, but they should not silently decide who remains authorized after handover.
Protect the accepted system after handover
A practical LED display access control plan connects roles, accounts, approvals, backups, testing, and review. It lets operators work efficiently while keeping higher-risk changes deliberate and recoverable. The result is not more paperwork for every button press; it is a known baseline, clear authority, useful evidence, and a safer route from a requested change to an accepted service state.
KSSdisplay can help project teams define the control boundary, role matrix, handover records, change workflow, recovery evidence, and support responsibilities for an LED installation. Review the available support resources or contact KSSdisplay with the application, system architecture, user roles, control platforms, remote-support needs, delivery location, and target handover date.